Kraftlinie Gard provides continuous visibility across SAP security, access and risk. Turn fragmented technical data into prioritised exposure, traceable evidence and actionable governance — without taking change control away from your SAP teams.
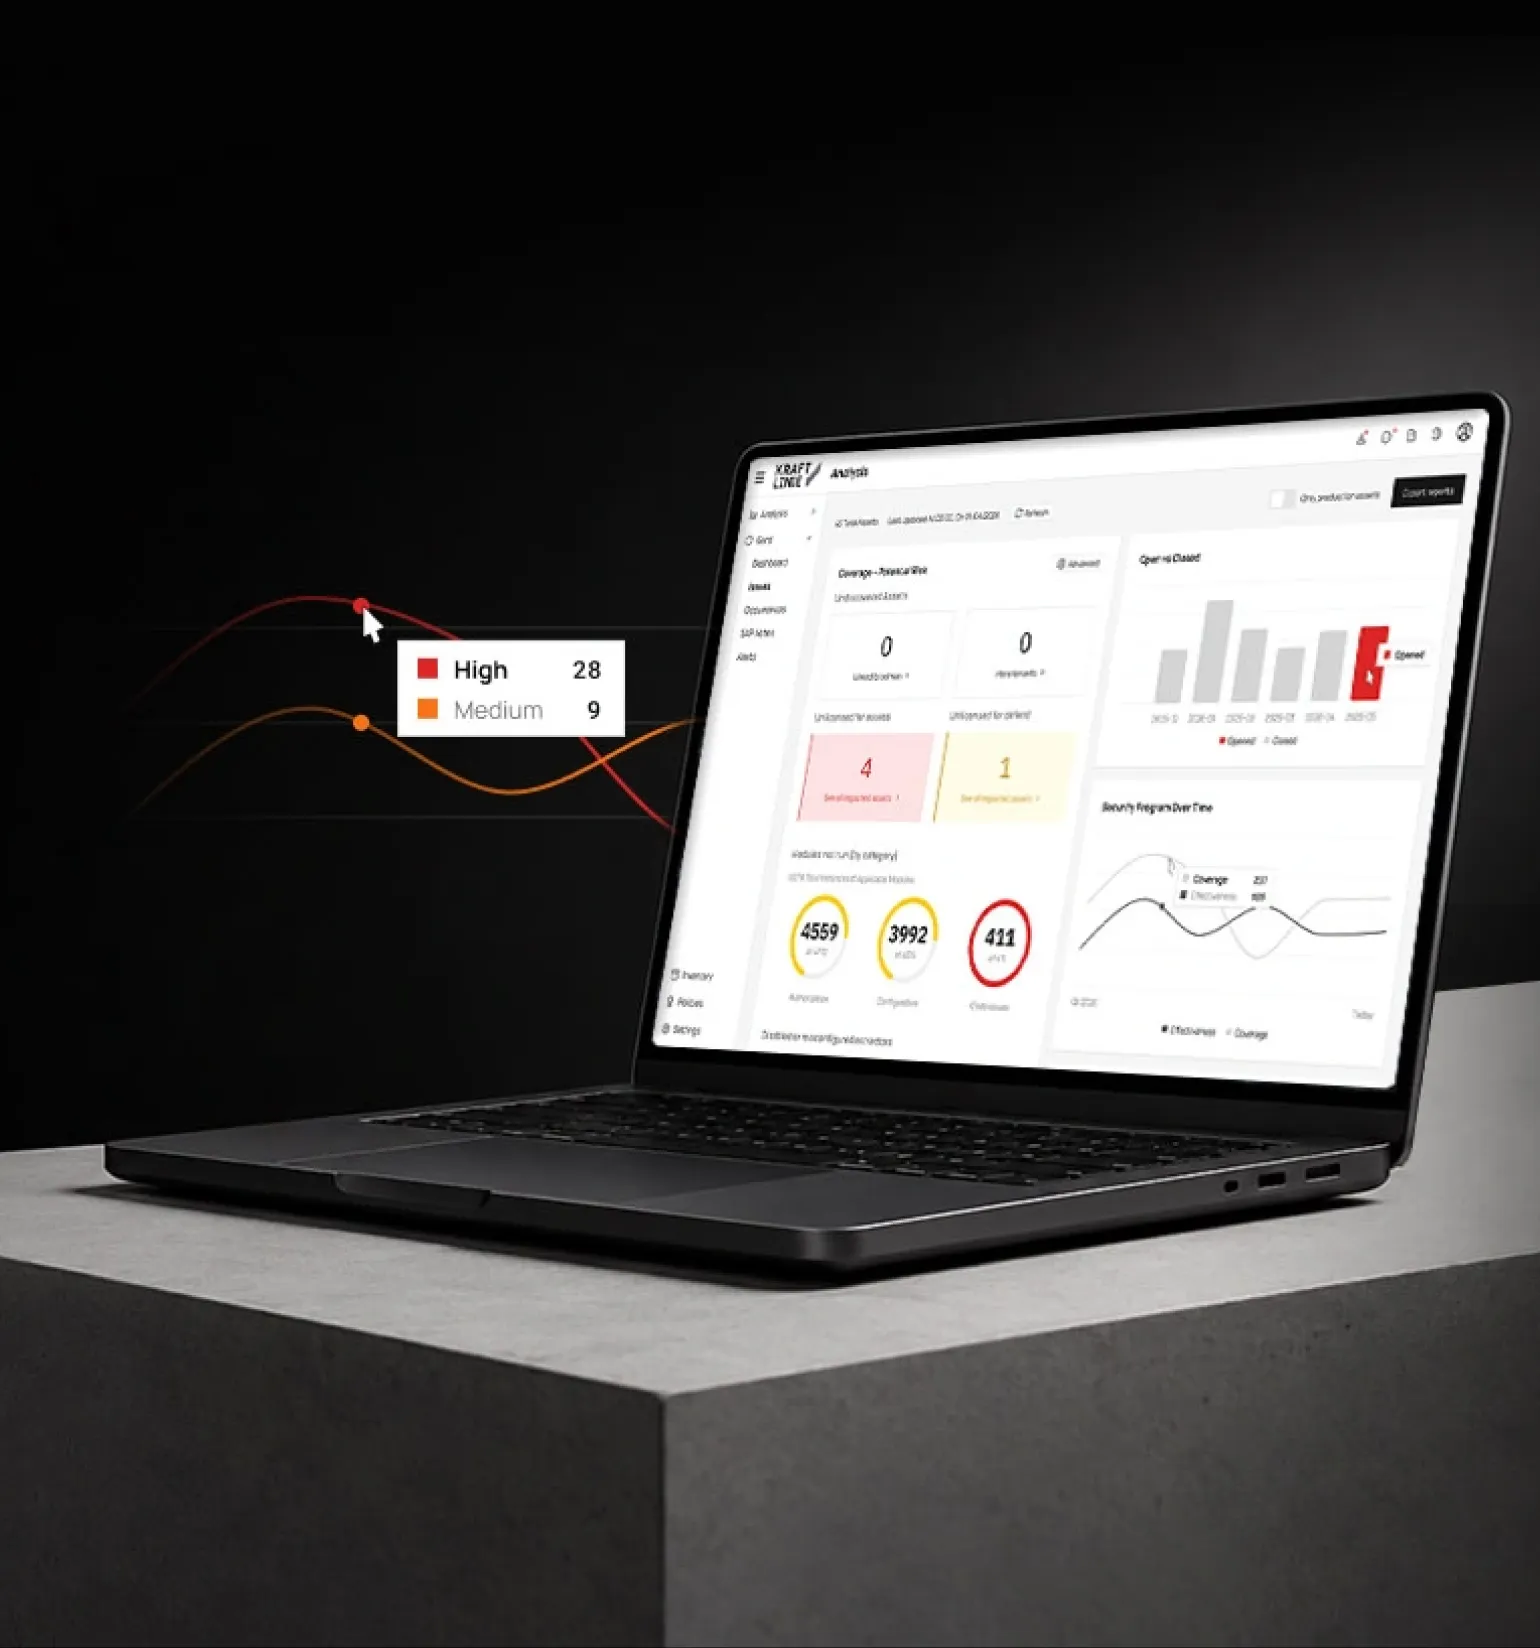
SAP environments combine critical business processes, thousands of users and roles, complex authorisation models, security configurations, services, logs and continuous platform change. When governance relies on periodic audits, manual checks and disconnected spreadsheets, material exposure can remain invisible until it becomes an operational or compliance issue.
The risk is not only a sophisticated cyber threat. It can also be a misconfiguration, an exposed service, an unpatched security note, excessive access, an incompatible combination of permissions, or a control dependency that is not being monitored consistently.
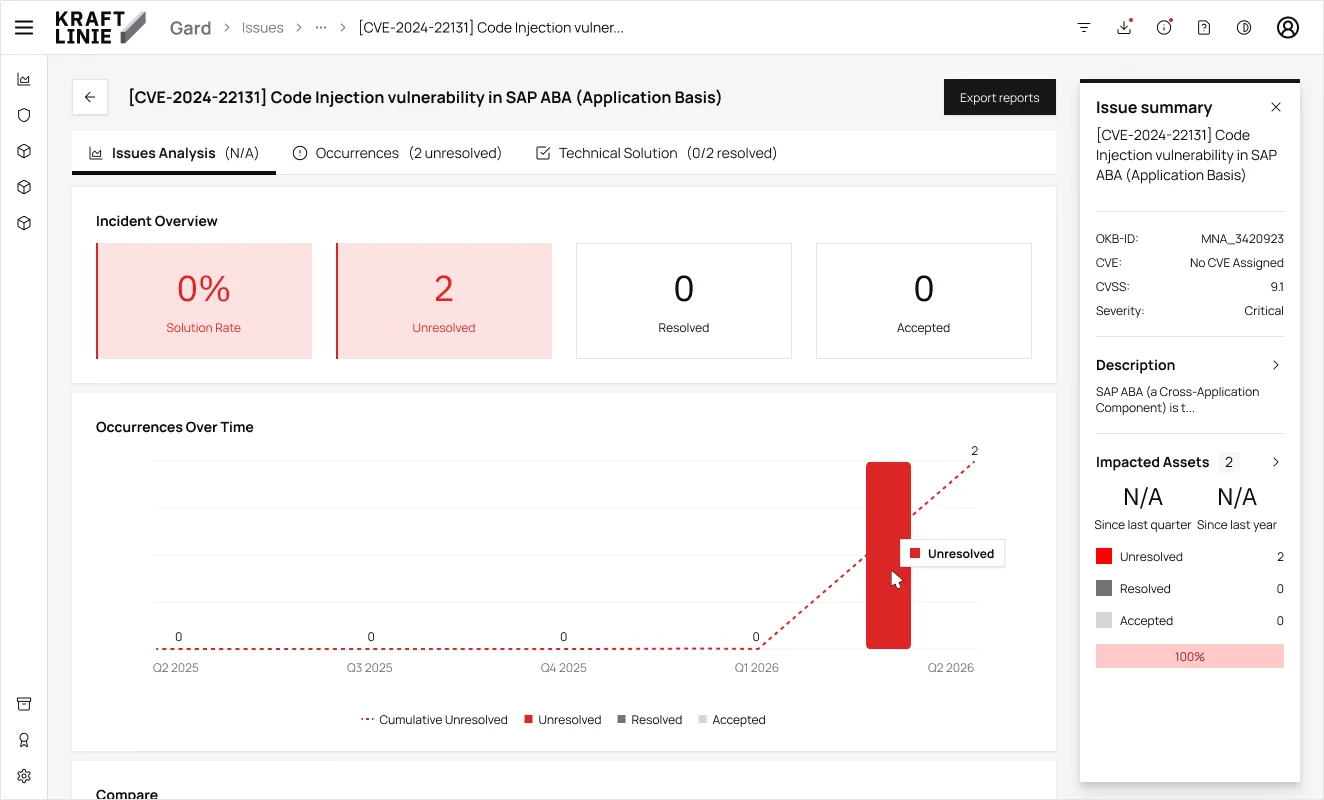
Continuous SAP security posture visibility across critical configurations, security notes, exposed services, audit logs and technical security signals.
Access visibility across users, roles and authorisations, designed to support stronger SAP access governance and clearer ownership.
Risk analysis designed to connect SAP access actions and incompatible rule combinations to Segregation of Duties and sensitive-access exposure.
Audit-ready evidence, control traceability and reporting designed to support internal compliance and external assurance activities.
Operational tracking from identified exposure to ownership, recommended treatment, evidence and follow-up.
Gard Security
Continuously assess security-relevant SAP parameters and configurations against established baselines and required standards.
Track the implementation status of relevant SAP security corrections and prioritise remediation based on exposure.
Identify active HTTP services and monitor potential exposure that can increase the SAP attack surface.
Analyze security audit log events to identify critical activity, anomalous behaviour and events that require investigation.
Enrich internal SAP security posture with external vulnerability and threat context to improve prioritisation.
Maintain persistent visibility across security-relevant conditions instead of relying only on periodic assessments.
Kraftlinie Gard is designed to correlate users, roles, authorisations, actions and risk rules so access exposure can be analysed with business context instead of isolated technical records.
Analyse incompatible access combinations and trace each materialised risk back to the SAP user, role, authorised action, rule and business-risk context.
Identify structural conflicts embedded within a single SAP role.
Identify conflicts created by the combination of different roles assigned to the same user.
Preserve the relationship between user, role, transaction or action, rule combination, severity, process and resulting risk.
Deduplicate technical evidence into decision-ready user-and-risk results while preserving detailed drill-down for audit and remediation.
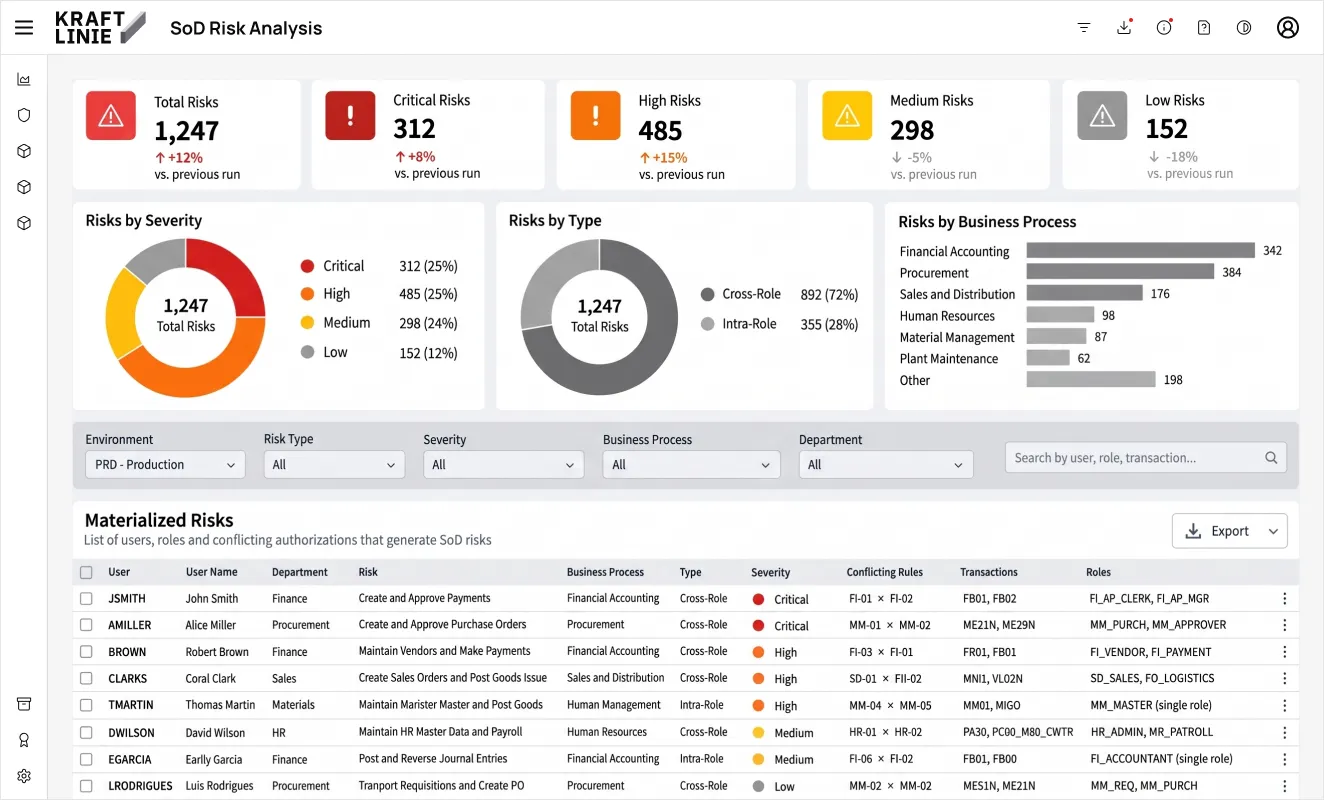
Executive SoD Cockpit — Consolidated visibility of materialised risks, exposed users, active roles, authorised transactions, and risk distribution by severity, business process and department. Illustrative product view. Values shown are sample data.
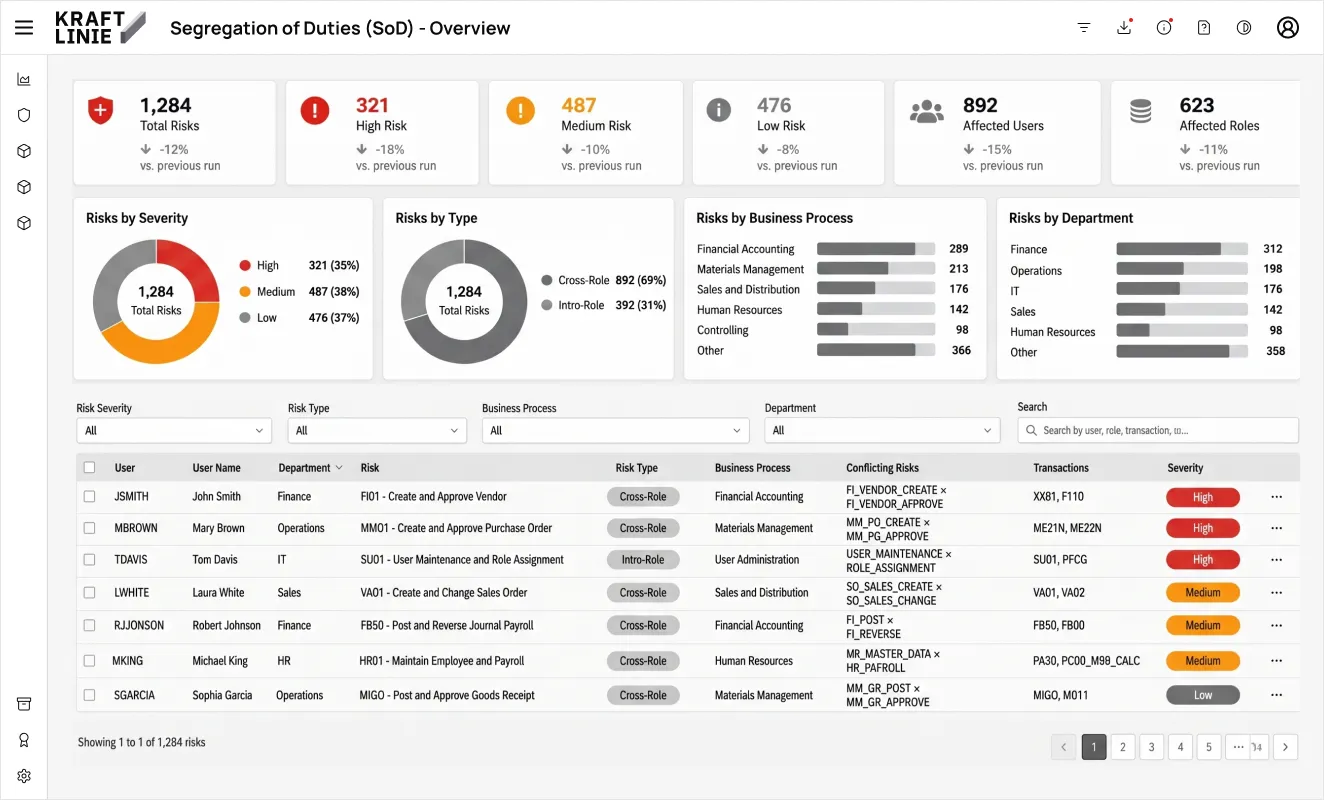
Materialised Risk Evidence — A single view connects risk, user, department, conflicting rules, transactions and conflict type, supporting traceable analysis and informed action. Illustrative product view. Values shown are sample data.
Establish controlled, read-only connectivity to the SAP landscape and collect the security, configuration and access data required for the enabled capabilities.
Evaluate technical conditions and access evidence against configured baselines, rules and risk logic. Separate noise from exposures that require action.
Deliver prioritised findings, ownership context, recommended treatment and traceable evidence for remediation and audit readiness.
Read-only assessment helps preserve production stability while providing continuous visibility into security-relevant conditions.
Secure RFC connectivity with a limited authorisation profile aligned to the data required by the enabled capabilities.
No agent installation required on SAP application or database servers for the current monitoring approach.
Kraftlinie Gard provides diagnostics, evidence and recommended mitigation while SAP teams retain control over changes applied to production.
Built for SAP Security, SAP Basis, Cybersecurity, Internal Controls, GRC, Audit and business process owners who need a consistent view of SAP exposure and evidence.
No. The current monitoring architecture is read-only. Kraftlinie Gard provides diagnostics, evidence and recommended mitigation while your SAP teams retain control over production changes.
The current approach uses standard, secure RFC connectivity with a limited authorisation profile designed to collect only the information required by the enabled capabilities.
No endpoint agent installation is required on SAP application or database servers for the current monitoring approach.
The platform is designed to preserve structured evidence, execution context and traceability so Security, Internal Controls and Audit teams can review what was identified, how it was classified and how it was addressed.
Kraftlinie Gard includes an evolving access-risk capability designed to materialise SoD exposure from SAP users, roles, authorised actions and rule combinations. Availability depends on the product release and enabled module.
Fiori access analysis is part of the advanced access-governance roadmap, designed to correlate Fiori content with technical start authorizations and SAP authorization evidence.
Kraftlinie Gard is positioned as a focused SAP governance, risk and security platform. The right architecture depends on the customer’s governance scope, workflow requirements, integration landscape and control model.
Need to evaluate your current landscape or have technical questions about the platform’s architecture? Speak directly with our experts.
© 2026 Kraftlinie. All rights reserved. – Privacy Policy and Terms of Service